iamnetuseragent / demo-ghostprovider
Overview
GhostProvider is an open-source platform that simplifies self-hosting: paste a GitHub URL — deploy one of the supported services as a systemd service. Private, local, no third parties.
One-Click Deploy
Paste a GitHub URL — deploy one of the three supported services as a systemd service. Private, local, no third parties.
Requirements
- systemd (user-level)
- git
- Linux
Tech Stack
Rust/ratatui— TUI frameworkureq+rustls— HTTPS client locked to a compile-time host allowlistsystemd— user-level service management
Why systemd?
GhostProvider uses systemd user-level services because they provide:
- No root required — every user can manage their own services
- Auto-start on login — services survive reboots without manual config
- Clean removal — disable + delete unit file, cleans the repo & secrets file & lingering ports
- Sandboxing —
NoNewPrivileges,ProtectHome,ProtectSystem
This is the standard on Arch, Ubuntu, Fedora, Debian, and most modern Linux distributions.
Security Model
This is the security module GhostProvider uses — the necessary architecture for secure operation.
- All data stays local — every request goes through an HTTPS client locked to a compile-time host allowlist, recorded in
net.log, credentials never leave api.github.com - DNS that survives broken VPN/TUN setups — system
getaddrinfofirst, then transparent fallback to a DNS-over-HTTPS bootstrap atcloudflare-dns.com(pinned anycast IPs, Mozilla roots) - No root required — ordinary systemd user units, no sudo, nothing system-wide
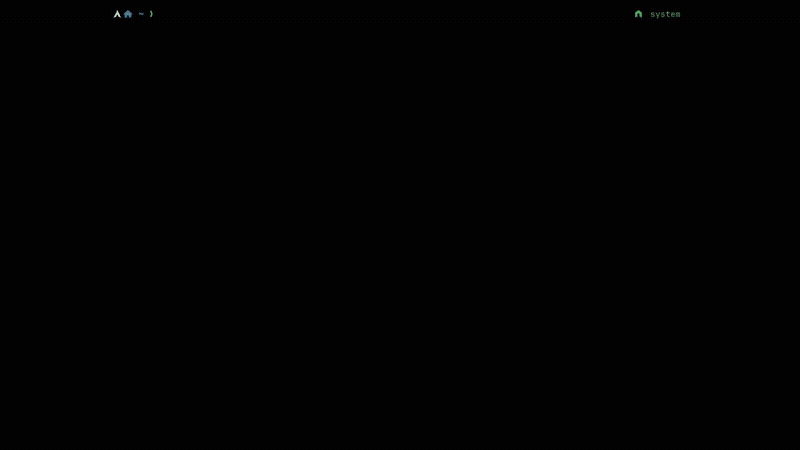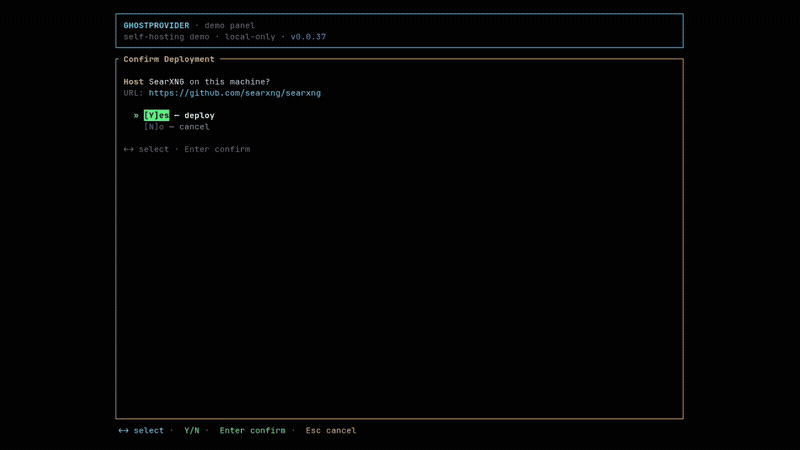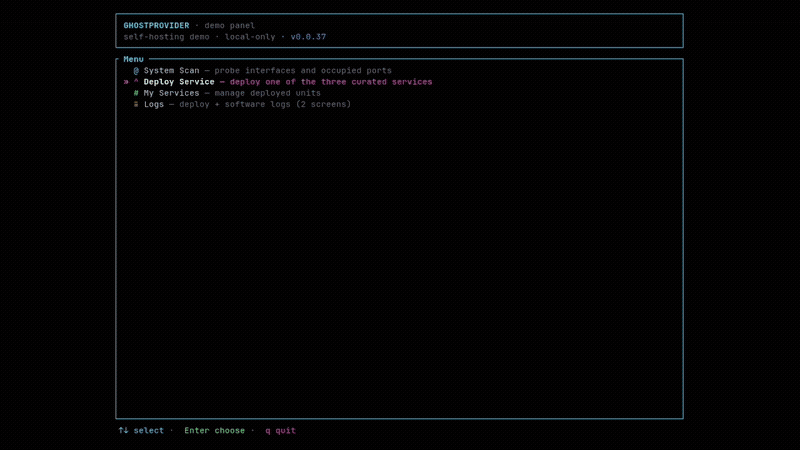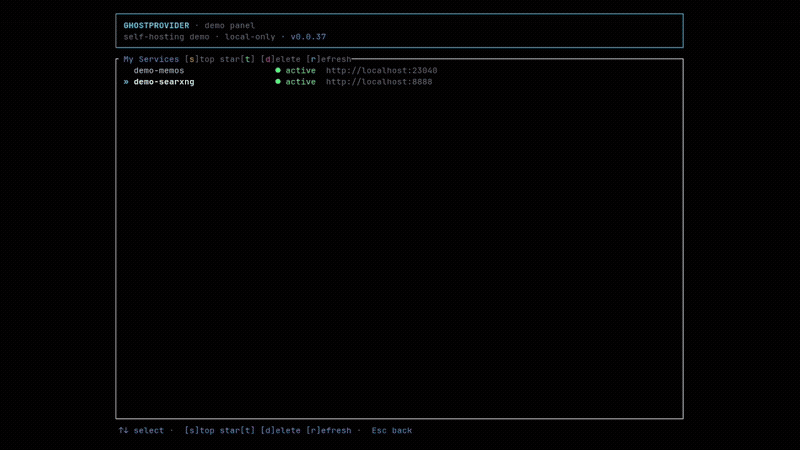
- Explicit confirmation before deploy — a deploy only starts after you explicitly confirm it
- Sandbox — builds run in a mandatory isolated environment; a deploy proceeds only when the sandbox verifies as FULL
- Pinned build tools — exact pinned releases, SHA‑256 verified, extracted into the project's
.ghost-cache;python3remains a hard requirement
System Scan
Scans your machine for prerequisites and maps occupied ports with their owning processes — nothing more. Deliberately: no VPN detection, no service fingerprinting, so the report stays useless to anyone but you.
- Prerequisites — do you have cargo, systemd, git installed?
- Listening ports — which ports are already in use?
- Known services — is SearXNG, Memos, or VERT already running?
This avoids port conflicts and helps GhostProvider choose the right deployment strategy. All data stays on your machine.
Control Panel
Full dashboard for all deployed services. Start, stop, restart, or remove — one click cleans the service, unit file, cloned repo, secrets file, and lingering ports.
Service Support
This is a restricted demo version of GhostProvider that only supports deploying the following services:
- VERT — github.com/VERT-sh/VERT
- SearXNG — github.com/searxng/searxng
- Memos — github.com/usememos/memos
Install
One command:
$ curl -fsSL https://raw.githubusercontent.com/iamnetuseragent/demo-ghostprovider/main/install.sh | sh
The installer is signed (install.sh.minisig) and fails closed by default: it downloads the release and its minisign signature, verifies it, and only then installs.
Usage
# launch the interactive panel
demo-ghostprovider
# allowlist + session request counters
demo-ghostprovider --show-endpoints
# E2E check against live systemd (loopback only)
demo-ghostprovider --selftest
# audit the build sandbox under strace
demo-ghostprovider --verify-sandbox
# print version
demo-ghostprovider --version
Uninstall
The same installer is the uninstaller. It fully removes the binary, all demo-* systemd user units, the deploy registry/secrets state and installed service data:
$ curl -fsSL https://raw.githubusercontent.com/iamnetuseragent/demo-ghostprovider/main/install.sh | sh -s -- --uninstall